WAVLINK WN551X3-A router flaw: critical command injection with a public exploit
CVE-2026-120345 lets a remote attacker run commands on the WAVLINK WN551X3-A. A proof of concept is public and no fix is listed.
By Andrew Ingleton · Published
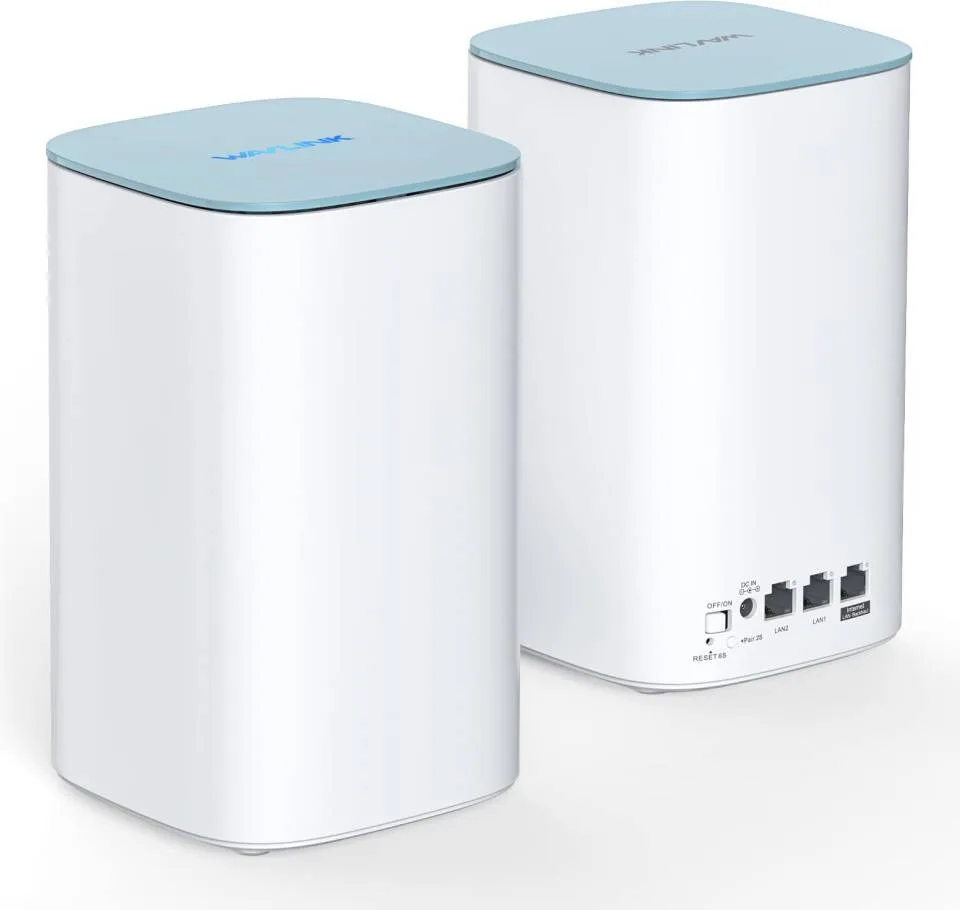
A critical command-injection flaw has been published for the WAVLINK WN551X3-A router, and a working proof of concept is already public. At the time of writing we have found no vendor fix and no evidence of attacks in the wild, so if you own one, the sensible move is to reduce its exposure now rather than wait.
What has been published
The flaw is tracked as CVE-2026-120345 and was added to the US National Vulnerability Database on 2 November 2026 by the vulnerability database VulDB. The record describes an OS command injection in the DNS resolution handler of firmware M51X3_V251020-WO-182e965 (the function sub_41a430 in /bin/ioos). By manipulating an argument called data, an attacker can run commands on the device, and the description says the attack can be started remotely. The record also says the exploit has been made public and that the vendor was contacted early about the disclosure.
How serious is it?
| Item | What the NVD record shows |
|---|---|
| Severity | 9.3 Critical (CVSS 4.0 score supplied by VulDB). NVD itself has not yet provided an assessment and says the record is not scheduled for enrichment. |
| Attack conditions | Network, low complexity, no privileges and no user interaction |
| CISA assessment (added 5 November) | Exploitation: proof of concept. Automatable: yes. Technical impact: total. |
| Weaknesses | CWE-77 and CWE-78 (command and OS command injection) |
| Fix | None listed in the record |
Some secondary coverage has described this as "actively exploited" with a score of 10.0. The NVD record itself shows a public proof of concept and a 9.3 score from VulDB. CISA's wording is "proof of concept", not confirmed exploitation, so we are describing it that way.
What to do if you have one
- Check the model and firmware in the router's admin page. Only the WN551X3-A on the firmware above is named in the record; we do not know whether similar WAVLINK models share the code.
- Turn off remote administration and make sure the admin page is not reachable from the internet.
- Keep it away from anything important: do not use it as your main router, or put it on an isolated network, until a fix appears.
- Look for firmware from WAVLINK and install it as soon as it is released.
- If no fix arrives, replace it with a model that still receives updates. Our router comparison is a starting point.
The wider lesson
Low-cost routers and extenders often get few firmware updates, and a public exploit appears long before a patch. When you choose one, check how long the maker has supported its products, not only the speed on the box.
Sources: National Vulnerability Database record for CVE-2026-120345 (published 2 November 2026, modified 5 November 2026), which cites VulDB.